A data sheet tells you a device runs at -40 to 75°C. It does not tell you whether that rating holds inside a sealed enclosure next to a motor radiating 60°C on its own. It does not tell you how the firmware gets patched, who discloses vulnerabilities, or what happens to your production data when the manufacturer sunsets the product in Year 4 of a 15-year line. The gap between advertised specs and actual industrial IoT device requirements is where deployments fail.
The IIoT market is projected to exceed $1 trillion by 2035, and global connected IoT devices are already past 20 billion. Devices are shipping fast. Whether they survive and stay secure for their full service life depends on requirements most procurement specs cover only partially.
I deploy IoT hardware across aviation, logistics, and industrial operations. The pattern repeats: teams specify a temperature range, pick a wireless protocol, connect a cloud dashboard, and call it done. Then Year 2 arrives with a firmware vulnerability nobody can patch, a dead battery in a location that requires scaffolding to reach, or an interoperability gap that turns a “connected” device into a data island. This article is the checklist that prevents those failures.
“Industrial Grade” Does Not Mean What You Think
There is no universal certification called “industrial grade.” NIST’s operational technology security guidance makes this explicit: OT systems have distinct performance, reliability, and safety requirements because they interact with the physical environment. What qualifies a device depends entirely on where it operates, what it controls or measures, and what happens when it fails.
Temperature is one variable among many. A device rated for extended cold and heat might still fail if humidity condenses inside the housing, if vibration loosens a connector, or if EMC interference from a variable-frequency drive corrupts its readings. Each of those is a separate qualification with its own test standards.
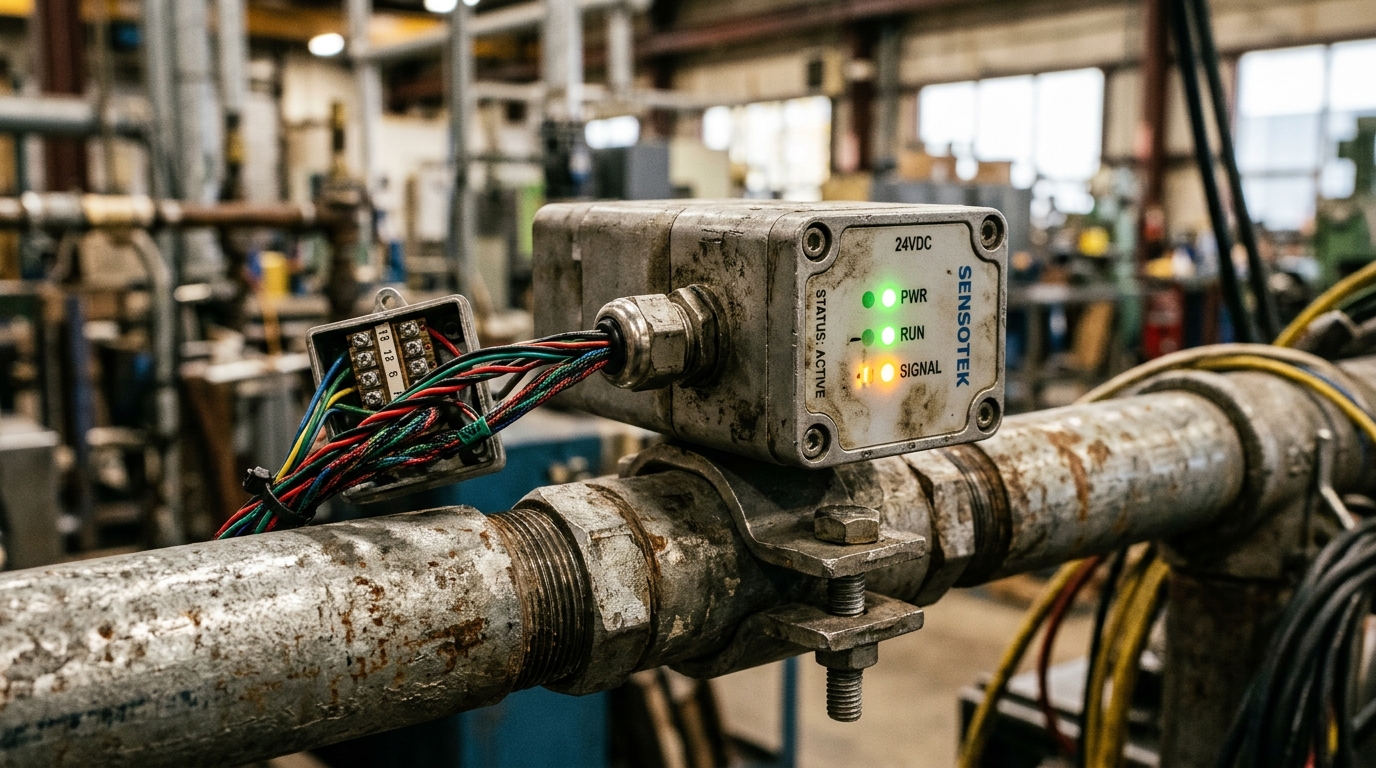
Consider two real products. Siemens’ SIMATIC IOT2050 operating instructions classify it as “open equipment” under UL 61010-2-201, meaning it must be installed inside an enclosure that protects against mechanical hazards, electric shock, and fire spread. If your deployment plan does not include that enclosure, your system is noncompliant from day one. The device is capable. The data sheet just does not do the system-design work for you.
Advantech’s EKI-2710E-2CI industrial switch lists IP30 protection, -40 to 75°C, 5 to 95% non-condensing humidity, UL62368-1 safety, and specific EMC/EMS test results. Those are detailed, testable specs. But “non-condensing” is a real constraint. Mount it in a tropical port environment with condensation cycles, and the humidity rating becomes the weak link in your design.
The rule for procurement: do not accept “industrial grade” as a line item. Require evidence for each environmental dimension of your specific site. Temperature, humidity (condensing or not), vibration profile, shock, dust, water ingress, altitude, corrosive atmosphere, and hazardous-location classification. Each one is a pass/fail criterion.
Six Device Security Capabilities to Require Before Purchase
Cybersecurity is not a network overlay you add after deployment. It is a device capability you specify before buying. NISTIR 8259A defines six baseline capabilities every connected IoT device should support. Here is how to turn them into RFP language:
| Capability | What it means | Question for your RFP |
|---|---|---|
| Device Identification | Unique logical and physical identity | Can you inventory serial number, network identity, model, and firmware version without a manual spreadsheet? |
| Device Configuration | Only authorized entities change settings | Are changes authenticated? Can approved configurations be backed up and restored? |
| Data Protection | Stored and transmitted data protected from unauthorized access | Which data is encrypted, where are keys stored, and what remains in cleartext? |
| Logical Access | Interfaces limited to authorized entities | Can unused ports and services be disabled? Can remote access be restricted to approved paths? |
| Software Update | Secure, configurable update mechanism | Are updates authenticated? Is rollback documented? Are patch windows compatible with your plant operations? |
| Cybersecurity State Awareness | Device reports its security status | Can firmware version, configuration state, and security events be monitored by the operator? |
If this feels abstract, consider what happens without it. CISA issued an advisory for Unitronics Vision and Samba PLCs carrying a CVSS score of 9.8 (near-maximum severity). The root cause: insecure defaults. The devices shipped with default credentials that operators never changed, and some were exposed directly to the public internet. CISA’s recommended fixes read like a basic device-security checklist. Change default passwords, restrict remote access, use firewalls, back up configurations, keep firmware updated. Every one of those maps to the NISTIR 8259A capabilities above.
At larger scale, the consequences multiply. Norsk Hydro’s 2019 cyberattack affected global operations, with estimated total costs around NOK 800 million. Extruded Solutions, the most affected business area, suffered significant production losses. Other areas maintained near-normal output only through labor-intensive manual workarounds. The lesson for device requirements: local autonomy and documented manual fallback are not optional features. They are continuity requirements. If your IIoT device depends entirely on an enterprise network or cloud connection to function, you have a single point of failure in your production line.
NIST updated this thinking in April 2026. IR 8259 Revision 1 recommends that manufacturers address pre-market cybersecurity activities and provide support through end-of-life, including vulnerability disclosure, update delivery, and customer communication. This is your leverage at the negotiating table. Before purchase, ask: how long will you support this device? How will you notify us of vulnerabilities? What is your update cadence? Vague answers mean the device is a liability with a countdown timer.
Connectivity Is a Site Decision, Not a Technology Bet
The Ethernet vs. fieldbus vs. Wi-Fi vs. 5G debate generates more marketing decks than useful guidance. HMS Networks’ 2026 analysis of newly installed factory-automation nodes provides actual proportions:
- Industrial Ethernet: 79% of new nodes (up from 76% in 2025)
- Fieldbus: 14% (down from 17%)
- Wireless: 7% (flat year-over-year)
That 7% wireless share is often misread. It counts newly installed factory-automation nodes in HMS’s analysis, not the wireless market overall. A separate commercial estimate puts wireless connectivity at 58.60% of the broader IIoT market by segment. These are not contradictory. They measure different things: one counts deployed protocol nodes on factory floors, the other describes a market-revenue category.
Ethernet dominates where you need deterministic control, established protocol ecosystems, and proven plant integration. Fieldbus persists because brownfield equipment does not disappear on a vendor’s timeline. Wireless earns its place where mobility, retrofit constraints, or cable-access problems justify it. HMS notes that private 5G deployment remains slower than expected, with network complexity cited as a primary barrier.
For lower-complexity cellular use cases, GSMA’s 2025 paper describes 5G RedCap (Release 17) and eRedCap (Release 18). eRedCap caps throughput at 10 Mbps while reducing device cost and energy consumption. Useful for telemetry and non-real-time data collection. Not a substitute for wired machine control.
On the other end of the spectrum, Ethernet-APL and 10BASE-T1L are already operating in process-automation installations, extending single-pair Ethernet toward field-level devices that previously required proprietary fieldbus connections. An Ethernet-APL Power Class B supporting up to 1.16 W opens the door for powered field instruments. But standards maturity, device availability, and hazardous-area certification still need to be verified project by project.
The procurement rule: do not choose connectivity based on what is newest. Choose based on your control timing requirements, installed base, mobility needs, site coverage, power budget, and risk tolerance. Then require a site RF survey and interoperability test before committing to any wireless path.
Power, Lifecycle, and Field Maintainability
A device that needs five years of battery life in a location serviced once a year has a completely different power budget than a cabinet-mounted gateway on 24V DC. Yet procurement specs routinely omit power-consumption modeling, battery-replacement logistics, and energy-budget calculations.
In asset tracking (where I spend most of my working hours), power is the constraint that shapes everything. A GPS tracker on a reusable container, a ULD, or a piece of ground-support equipment needs to last years, not months. That means choosing between cellular check-in intervals, GNSS fix frequency, and accelerometer wake-up sensitivity. Every parameter trades battery life against data resolution. The requirement is not “long battery life.” It is “X location reports per day for Y years with Z% reliability at ambient temperatures between A and B.” Anything less specific invites disappointment.
Lifecycle mismatch is the silent requirement killer. Industrial equipment commonly runs 10 to 20 years. The IoT device attached to it lives in a different upgrade cycle. Firmware, communication protocols, cloud platform APIs, and cellular network generations all change faster than physical hardware. The question to answer at procurement: what happens when the 4G network your tracker relies on gets sunset? What happens when the cloud platform’s API version is deprecated? Who absorbs the integration cost?
NIST’s IR 8259 Revision 1 gives you contractual language for this. It recommends that manufacturers define support periods, vulnerability disclosure processes, update delivery mechanisms, and end-of-life procedures before the device reaches market. Translate that into your RFP: require commitments with dates, not promises with adjectives.
Then there is the requirement most engineers forget because they spec devices at a desk, not on a ladder in the rain. Field maintainability. Can a technician identify the device, access its mount, swap a battery or replace the unit, and confirm it is back online without specialized tools or a laptop? In aviation ground operations, a tracker on a dolly or cargo container gets knocked, soaked, and baked in jet exhaust. The mounting hardware, the housing durability, and the replacement procedure matter as much as the sensor’s RF performance. If swapping one device takes 45 minutes and a software reconfiguration, multiply that by your fleet size and you will see why maintainability belongs in the spec.
Compliance Deadlines Already Running
Regulatory requirements for connected devices have moved from theoretical to enforceable. If you sell, integrate, or deploy IIoT products in Europe, the clock is already past zero on some obligations.
The EU Cyber Resilience Act’s reporting obligations took effect on September 11, 2026. Manufacturers of products with digital elements must now report actively exploited vulnerabilities and severe incidents. The CRA’s main obligations (security requirements across the product lifecycle, including vulnerability handling, secure defaults, and documented support periods) apply from December 11, 2027. If your supplier cannot describe their CRA compliance plan today, they are already behind schedule.
In the United States, the picture is different. The FCC’s Cyber Trust Mark is voluntary and explicitly covers consumer wireless IoT products. It excludes products primarily used for manufacturing, industrial control, or enterprise applications, and it excludes wired devices entirely. Do not list Cyber Trust Mark compliance as an industrial procurement requirement. It was not designed for that purpose.
For aviation and airfreight, certification requirements are more specific and long-established. DO-160 (Environmental Conditions and Test Procedures for Airborne Equipment) governs what electronic devices can operate in or near aircraft. Any tracker, sensor, or gateway deployed in an airfreight or ULD tracking scenario must meet the relevant DO-160 sections, or it does not fly. This is not something you retrofit after purchase. The Thingfox T2 carries DO-160 approval specifically for airfreight use, which is why we deploy it in cargo and ULD tracking where uncertified devices simply are not allowed.
The practical action: map every applicable regulation and certification to your deployment geography and vertical before finalizing your device shortlist. Build compliance evidence into the procurement contract. If the device crosses borders, flies on aircraft, or enters hazardous areas (ATEX, IECEx), the certification is not a nice-to-have. It is a gate.
From Requirements to RFP: A Practical Checklist
Theory is useful. A spec you can paste into a procurement document is better. Below is a framework for translating industrial IoT device requirements into testable RFP language. Adapt each row to your specific process, environment, and risk profile.
| Requirement area | What to specify | Evidence to require from the vendor |
|---|---|---|
| Function and measurement | Measurand, range, accuracy, resolution, sampling interval, alarm behavior, timestamp quality | Acceptance test under your actual process conditions, not only the manufacturer’s lab report |
| Physical environment | Operating and storage temperature, humidity type, vibration, shock, dust, water ingress (IP rating), corrosive atmosphere, hazardous-location class | Third-party test certificates matching your site profile. Clarify whether enclosure is included or required separately. |
| Power and installation | Supply voltage range, surge/brownout tolerance, battery life at your usage profile, mounting method, thermal dissipation, service access | Battery-life calculation at your specific reporting interval and temperature range. Mounting hardware documentation. |
| Connectivity and interoperability | Physical layer, protocol, gateway requirements, data model, latency needs, network segmentation support | Interoperability test on your PLC, SCADA, historian, or edge platform. Site RF survey for wireless deployments. |
| Cybersecurity | NISTIR 8259A six capabilities, unique credentials, restricted remote access, authenticated updates, vulnerability disclosure process | Manufacturer security documentation, penetration test results (if available), defined patch and support policy |
| Lifecycle and support | Support duration, update delivery cadence, vulnerability notification, spare-part availability, end-of-life notice period, data export at retirement | Contractual commitments with defined timelines. Software bill of materials where available. |
| Compliance and certification | EU CRA readiness, applicable safety standards, EMC, industry-specific certs (DO-160, ATEX, IECEx), radio type approvals per deployment region | Current certificates for your deployment geography. Manufacturer’s CRA compliance roadmap with dates. |
One more line item that does not fit neatly into a table: require a system-level integration test before full-scale deployment. A device that passes every individual spec on paper can still fail when combined with your existing controllers, network infrastructure, and software stack. The integration test is where interoperability gaps, timing conflicts, and data-model mismatches surface. Better to find them with 10 units than with 10,000.
Frequently Asked Questions
What are the minimum requirements for an industrial IoT device?
There is no universal minimum. At a baseline, specify the device’s function and measurement needs, environmental ratings for your specific site, power budget, connectivity protocol, the six cybersecurity capabilities defined in NISTIR 8259A, and manufacturer support commitments including update delivery and end-of-life procedures. Derive every requirement from your process conditions and the consequence of device failure.
Is an IP rating enough to qualify a device as industrial?
No. An IP rating covers dust and water ingress but says nothing about temperature range, vibration, EMC immunity, electrical safety, or hazardous-location suitability. A device can be IP67 and still fail from condensation, RF interference, or power surges. Require separate evidence for each environmental dimension.
Should I choose Ethernet, fieldbus, or wireless for IIoT?
Choose based on control timing, installed base, mobility requirements, and power constraints. Industrial Ethernet accounts for 79% of new factory-automation nodes in 2026 (HMS Networks). Fieldbus persists in brownfield plants. Wireless fits mobile equipment, retrofits, and hard-to-cable locations. A site survey and interoperability test should precede the decision.
Which cybersecurity regulations apply to industrial IoT in 2026?
In the EU, the Cyber Resilience Act’s reporting obligations are active since September 2026, with full product-lifecycle requirements effective December 2027. In the US, the FCC Cyber Trust Mark is voluntary and excludes industrial devices. NIST IR 8259 Revision 1 provides manufacturer guidance. Verify sector-specific regulations (aviation, energy, hazardous locations) for your deployment.
How long should a manufacturer support an IIoT device?
Match support duration to your operational lifecycle. Industrial equipment runs 10 to 20 years, so a device with 3 years of firmware support creates a gap. Require contractual commitments for update delivery, vulnerability disclosure, spare parts, and end-of-life notification. NIST IR 8259 Rev 1 recommends manufacturers define these commitments before sale.
Does my IIoT device need to work if the cloud goes offline?
If production, safety, or asset tracking depends on local operation, yes. Specify local control, data buffering, alarm handling, and safe fallback modes. Do not place a safety-critical function in a cloud-dependent path unless the full system is independently validated for that architecture.
If your current device fleet disappears from view the moment it leaves your facility, or your RFP still treats “industrial grade” as a checkbox, the requirements above are a starting point. We build asset tracking solutions around devices that meet these criteria in aviation, logistics, and industrial operations. If you want to talk specifics for your environment, reach out to our team or explore our asset tracking device catalog to see what field-proven hardware looks like.

 +1 508 292 2210
One Response